
9 Best Security Compliance Tools for SAAS Companies in 2026, Compared
Compare the 9 best security compliance tools for saas companies on price, frameworks and evidence automation, with every price checked November 7, 2026.
 Shamim Mia, Founder, SerpAstraLast verified November 7, 202614 min read
We compare pricing pages, documentation and public reviews. We never accept payment for rankings.
Key takeaways
- Vanta is the best fit for most SaaS teams at $14,000/year; Drata follows at $15,000/year for engineering-led teams, and Secureframe at $7,500/year for teams that want guided setup.
- Comp AI is the only free option — its self-hosted open-source edition costs $0 — while every other tool here charges at least $7,500 a year before the audit.
- The single most important buying factor is what the starting price leaves out: the audit is sold separately on every paid tool except Thoropass, and extra frameworks add $2,000 to $7,500 a year each.
- Only Secureframe publishes a starting price on its own pricing page; the other paid figures come from vendor AWS Marketplace listings or, for Hyperproof, the price supplied to G2.
- Budget year two, not year one: startup discounts expire, headcount bands rise, and a second framework can double the platform bill.
On this page
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|---|---|---|
| Vanta | SaaS teams that want the widest integration net and the largest auditor network for a first SOC 2 | $14,000/yr | No |
| Drata | Engineering-led SaaS teams that want a custom framework builder and testing-as-code workflows | $15,000/yr | No |
| Secureframe | Growth-stage SaaS companies that want guided setup and a named compliance manager for SOC 2 and ISO 27001 together | $7,500/yr | No |
| Sprinto | Early-stage SaaS teams that want the fastest guided path to a first SOC 2 at the lowest entry price | $9,500/yr | No |
| Scytale | SaaS startups running many frameworks that want a compliance expert guiding them from first attestation to renewal | $7,500/yr | No |
| Thoropass | Founders who want the compliance platform and the SOC 2 audit on one contract from a single vendor | $8,700/yr | No |
| Hyperproof | Mid-market SaaS programs that run many frameworks at once and want one evidence set to serve them all | $12,000/yr | No |
| OneTrust | Large SaaS companies running SOC 2 inside a wider privacy, risk and internal audit program | Custom quote | No |
| Comp AI | SaaS engineers and budget-conscious startups that want open source, self-hosting, or the lowest-cost managed path to a first audit | Free | Yes (self-hosted) |
Make one of these tools?
We re-check this list every quarter. Send a correction, request a review, or ask about a clearly labeled sponsored spot.
Request a listingThe best security compliance tools for saas companies
Vanta
Best for: SaaS teams that want the widest integration net and the largest auditor network for a first SOC 2
Vanta is the default shortlist pick for SaaS teams that want the widest evidence net: 400-plus integrations pull data from cloud, identity, HR and code tools, and automated tests check controls every hour — over 1,400 tests in published comparisons. Essentials covers one framework for teams of 1 to 20 employees, and the Trust Center is included, so customer security questionnaires get answered from one branded page instead of email threads.
The price to budget is not the $14,000 list figure alone. The audit is sold separately through an auditor network of more than 100 firms, and each extra framework and module adds to the bill, so a first year lands near $20,000, the median Vendr reports from 377 purchases. Buy Vanta when integrations and auditor choice matter most; buy Drata when engineers want to define their own controls.
What we like
- More than 400 integrations, the widest evidence net in this list
- More than 1,400 automated control tests run every hour
- Trust Center included, so security questionnaires are answered from one branded page
- Auditor network of more than 100 firms gives buyers real choice
Watch out for
- The audit is sold separately through a partner auditor network
- Essentials covers one framework for 1 to 20 employees — extra frameworks and modules add to the bill
- Typical first-year cost lands near $20,000, the median Vendr reports, not the $14,000 list figure

Drata
Best for: Engineering-led SaaS teams that want a custom framework builder and testing-as-code workflows
Drata is the pick for engineering-led SaaS teams: its custom framework builder lets you define controls when enterprise customers send bespoke questionnaires, and testing-as-code workflows fit teams that already treat infrastructure as code. It covers SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, CCPA and more, with more than 300 integrations and continuous control monitoring that flags drift the day it happens.
Foundation costs $15,000 a year for companies with 1 to 50 full-time employees and includes one pre-mapped framework; custom frameworks cost extra on every plan, and the audit is separate. Vendr's median contract is about $25,000 a year, so budget well above the entry figure for a second framework. Buy Drata when engineers will run compliance themselves; buy Secureframe when you want a person guiding the first audit.
What we like
- Custom framework builder defines controls for bespoke enterprise questionnaires
- More than 300 integrations with continuous control monitoring
- AI-native GRC features cover risk and vendor management beside compliance
- Audit alliance of more than 175 firms gives auditor choice
Watch out for
- Custom frameworks cost extra on every plan
- The audit is sold separately — budget for a CPA firm on top of the platform
- Vendr's median contract is about $25,000 a year, well above the $15,000 entry figure

Secureframe
Best for: Growth-stage SaaS companies that want guided setup and a named compliance manager for SOC 2 and ISO 27001 together
Secureframe is the most guided option in this list: a named compliance manager walks first-time buyers through setup, training is bundled, and the Fundamentals plan publishes a starting price of $7,500 a year for one framework. It covers SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR and CCPA with more than 300 integrations, and its federal depth — CMMC, FedRAMP and GovRAMP — suits SaaS teams selling to government customers.
Read the price carefully: the AWS Marketplace listing prices platform access and the first framework at $7,500 each, so a one-framework start costs about $15,000 a year together, and the audit is separate. Vendr's median contract sits near $20,000 a year. Buy Secureframe when guided setup matters more than the deepest integration list; buy Vanta when your stack is unusual and coverage comes first.
What we like
- The only tool here with a starting price published on its own pricing page
- Guided setup with training bundled and a named compliance manager
- More than 300 integrations and 40-plus frameworks
- Federal framework depth, including CMMC, FedRAMP and GovRAMP
Watch out for
- The AWS Marketplace listing prices platform and first framework at $7,500 each — $15,000 together
- The audit runs through a partner network rather than in-house
- Niche standards such as CMMC and SOX ITGC trail Vanta and Drata

Sprinto
Best for: Early-stage SaaS teams that want the fastest guided path to a first SOC 2 at the lowest entry price
Sprinto targets early-stage SaaS teams that want speed and a predictable bill: there is no per-user pricing, so costs do not climb as the team grows, and guided first-audit help plus a device agent and Jira sync suit remote teams without a compliance hire. It covers more than 200 frameworks, including SOC 2, ISO 27001, HIPAA, GDPR and PCI DSS, with more than 300 integrations.
The $9,500 starting figure is $7,500 for the Starter platform plus $2,000 for the first framework on AWS Marketplace, and the audit runs through partner auditors at a separate fee. Startup discounts run 60% off in year one, 50% in year two and 40% in year three, so model year three before signing — renewals rise as discounts expire. Buy Sprinto for the cheapest guided path to a first SOC 2.
What we like
- No per-user pricing, so costs stay flat as the team grows
- Guided first-audit help with a device agent and Jira sync for remote teams
- More than 300 integrations and 200-plus frameworks
- Startup discounts of 60% in year one, 50% in year two and 40% in year three
Watch out for
- The audit runs through partner auditors at a separate fee
- The entry tier caps AI questionnaires at 20 a year
- Startup discounts expire — renewals rise up to 40% by year three as discounts roll off
Scytale
Best for: SaaS startups running many frameworks that want a compliance expert guiding them from first attestation to renewal
Scytale suits SaaS startups running many frameworks at once: more than 60 frameworks are covered, and a compliance expert supports the team from first attestation through renewal rather than leaving them with a dashboard alone. Auditor matching helps teams without an existing auditor relationship, and the audit and penetration test are sold as add-ons — about $4,200 and $4,500 respectively in published guides.
The platform starts at $7,500 a year for the platform and one framework on AWS Marketplace, and the final quote scales with company size and framework count. Integration coverage near 100 to 150 tools trails the leaders, so teams with unusual stacks should verify coverage before buying. Buy Scytale when expert support matters more than the biggest integration list.
What we like
- More than 60 frameworks in one platform
- Compliance expert support from first attestation through renewal
- Auditor matching for teams without an existing auditor relationship
- Penetration test add-on, about $4,500 in published guides
Watch out for
- The audit is an add-on, about $4,200 in published guides
- Integration count near 100 to 150 trails the leaders
- Final quote scales with company size and framework count — the $7,500 figure is a floor
Thoropass
Best for: Founders who want the compliance platform and the SOC 2 audit on one contract from a single vendor
Thoropass is the only tool here that sells the platform and the SOC 2 audit on one contract: its auditors work inside the same workspace where the team collects evidence, through Thoropass Assurance, an affiliated CPA firm. A Compliance Architect guides readiness, and the platform covers SOC 2, ISO 27001, HIPAA, PCI DSS, HITRUST and CMMC with more than 100 integrations.
The platform starts at $8,700 a year including the first framework on AWS Marketplace, and the SOC 2 audit subscription starts at $5,800 a year — a $14,500 published starting point, though real contracts average about $30,000 a year. Note that G2 lists the audit from $11,500 a year, so get the audit price in writing. Buy Thoropass when one vendor for software and audit is worth a premium.
What we like
- Platform and SOC 2 audit on one contract — the only tool here that bundles both
- Auditors from an affiliated CPA firm review evidence inside the same workspace
- A Compliance Architect guides readiness, with biweekly project management reviewers praise
- Listed by the PCI SSC as both a QSA company and an ASV
Watch out for
- Real contracts average about $30,000 a year, well above the $14,500 published starting point
- G2 lists the audit from $11,500 a year, against $5,800 on AWS Marketplace — get it in writing
- Integration count near 100 trails the leaders, and some reviewers report a disjointed dashboard

Hyperproof
Best for: Mid-market SaaS programs that run many frameworks at once and want one evidence set to serve them all
Hyperproof fits mid-market SaaS programs that run many frameworks at once: one evidence set serves many standards, scheduled syncs keep evidence fresh, and a dedicated audit workspace lets the company's own auditor work inside the platform. More than 200 integrations cover the standard stack, and the value shows at renewal, when a second or third framework reuses evidence already collected.
Hyperproof publishes no price on its own site; the $12,000 a year figure is the price Hyperproof supplied to G2, so treat it as a starting point and get a written quote. There is no device agent, and guided onboarding trails Secureframe and Sprinto for first audits. Buy Hyperproof for a multi-framework program at renewal time; buy Sprinto or Secureframe for a first audit.
What we like
- One evidence set serves many frameworks — the value shows at renewal
- Dedicated audit workspace where the company's own auditor works
- More than 200 integrations with scheduled evidence syncs
- Centralized control management that reviewers praise for ease of use
Watch out for
- No published price on its own site — the $12,000 figure is supplied to G2, so get a written quote
- No device agent, unlike Vanta, Drata and Sprinto
- Guided onboarding trails Secureframe and Sprinto for first audits

OneTrust
Best for: Large SaaS companies running SOC 2 inside a wider privacy, risk and internal audit program
OneTrust is the enterprise option in this list: more than 50 frameworks sit under a collect-once, comply-many model, and the platform reaches beyond compliance into privacy, third-party risk and AI governance. It suits large SaaS companies running SOC 2 inside a wider risk and internal audit program, with many teams and many frameworks to coordinate, and it is trusted by over half of the Fortune 500.
No price is published, and implementation takes about two months on G2's Tech Risk and Compliance listing — this is a platform for teams with dedicated GRC staff, not a first-audit shortcut. Reviewers praise the breadth and regulatory intelligence but flag a steep learning curve and opaque pricing. Buy OneTrust when compliance is one workstream inside a larger governance program; buy anything else on this list for a standalone SOC 2.
What we like
- More than 50 frameworks under a collect-once, comply-many model
- Breadth beyond compliance into privacy, risk and third-party management
- Trusted by over half of the Fortune 500, per OneTrust
- Regulatory intelligence that reviewers praise for keeping programs current
Watch out for
- No published price — enterprise quotes only, and pricing is opaque
- Steep learning curve and heavy setup; needs dedicated GRC staff
- Overkill for early startups — implementation takes about two months
Comp AI
Best for: SaaS engineers and budget-conscious startups that want open source, self-hosting, or the lowest-cost managed path to a first audit
Comp AI is the open-source option: the core is published under AGPLv3, so a technical team can self-host it free and inspect the compliance engine, and the managed hosted plan is quote-only with a fixed fee that the vendor says covers the platform, the auditor and a penetration test. It covers more than 25 frameworks with over 500 integrations, and reviewers praise its automation and value for money.
Self-hosting costs nothing in licence fees, but someone has to deploy, patch, back up and secure it through the audit window, and the auditor network is smaller than Vanta's or Drata's. The hosted plan's price depends on frameworks, headcount and timeline, set on a pricing call. Buy Comp AI when engineers want open source or the lowest-cost managed path to a first audit.
What we like
- Free self-hosted open-source edition under AGPLv3 — the only $0 option here
- More than 500 integrations, the largest count in this list
- More than 25 frameworks with AI-driven evidence collection
- The managed plan's fixed fee covers the platform, auditor and a penetration test, per the vendor
Watch out for
- Self-hosting needs engineering time to deploy, patch, back up and secure
- The auditor network is smaller than Vanta's or Drata's
- The managed plan is quote-only, with the price set on a 20-minute pricing call
The best security compliance tools for saas companies turn SOC 2 and ISO 27001 from a spreadsheet slog into a system that collects evidence on its own. We ranked the nine tools below by fit for the most common buyer — a SaaS team preparing for a first SOC 2 audit — starting with the widest integration nets and ending with the free open-source option, and every price was checked on November 7, 2026.
How to choose the best security compliance tools for saas companies
- Start with the frameworks you must pass, in order. SOC 2 comes first for most SaaS teams selling to US customers; add ISO 27001 when European customers ask for it, and HIPAA or PCI DSS only when the product actually handles health data or card payments.
- Count frameworks, not users. Most tools here price by headcount band and framework count, and a second framework costs $2,000 to $7,500 a year extra — so the tool that is cheapest for one framework can be the dearest for two.
- Check the integration list against your real stack. Vanta lists more than 400 integrations and Comp AI more than 500, while Scytale and Thoropass sit near 100 to 150; an integration your stack needs that is missing means manual evidence uploads every quarter.
- Ask who does the audit, and what it costs. Only Thoropass bundles the audit into the contract; everywhere else the audit is a separate CPA fee, so get the auditor's price in writing before you sign for the platform.
- Weigh guided help against engineering time. Teams without a compliance hire should shortlist Secureframe, Sprinto or Scytale, where a person guides the first audit; engineering-led teams can save money with Drata or Comp AI and run it themselves.
Compliance is one system in your stack, not the whole stack. If the business also needs to be found online, our guide to SEO agencies for SaaS companies covers the visibility side. And before you publish new pages for the services you sell, run your titles through the free SERP snippet preview tool — it shows exactly how the title and description will look in Google.
Whatever you shortlist, try it with real data before you pay. Connect your cloud, identity and ticketing tools in a trial or demo, and check whether evidence actually collects automatically or needs manual uploads — that gap decides the real workload. Check two things before signing: that the headcount band covers your whole company, not just the engineering team, and that your auditor will work inside the platform rather than over email.
Security compliance tools for saas companies pricing: what you will actually pay
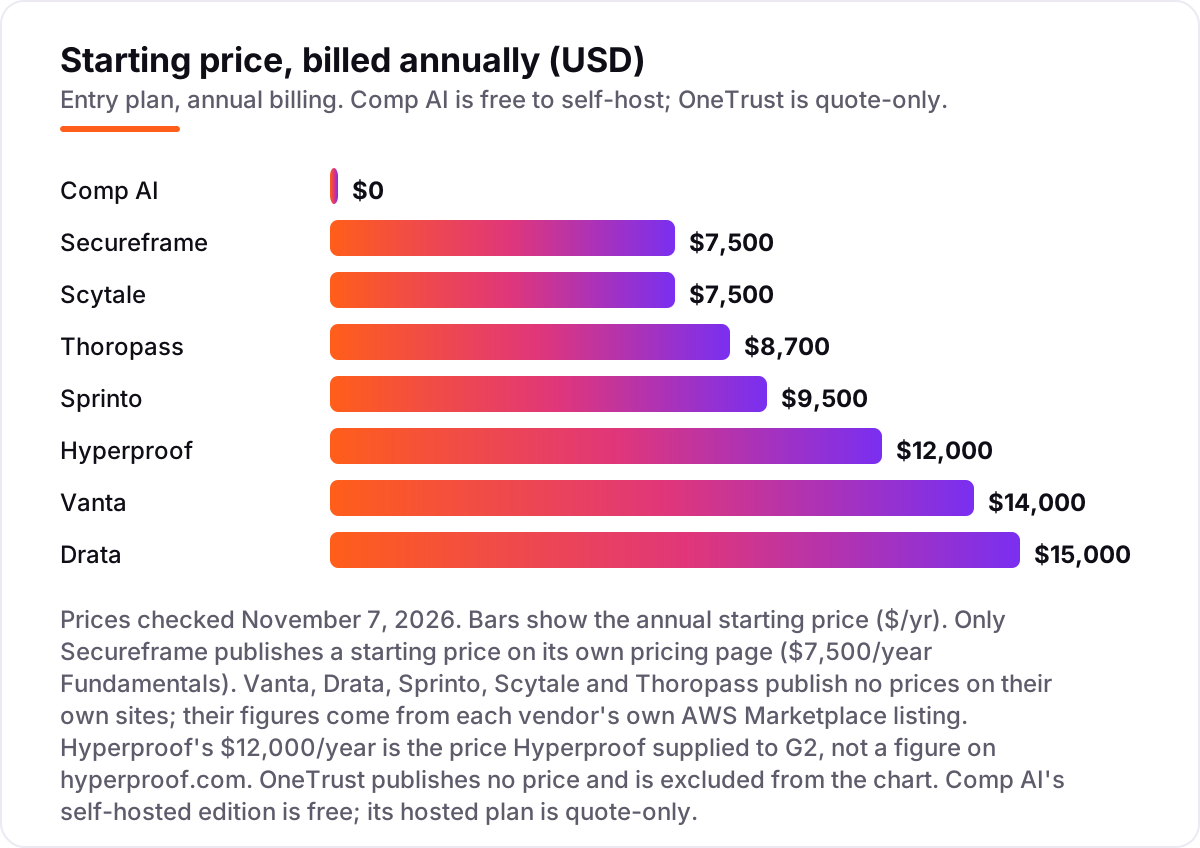
Take a 25-person SaaS team doing SOC 2 only, in year one, platform only. On list prices, the platform costs $0 on Comp AI self-hosted, $7,500 on Scytale or Secureframe Fundamentals, $8,700 on Thoropass, $9,500 on Sprinto, $12,000 on Hyperproof, $14,000 on Vanta Essentials and $15,000 on Drata Foundation, while OneTrust is a custom quote. Two of those numbers need adjusting before they are real: Secureframe's AWS Marketplace listing prices platform access and the first framework at $7,500 each, so a one-framework start costs about $15,000 a year together, and Comp AI's $0 covers the licence only — hosting and staff time are extra.
Then add the audit, which is the part first-time buyers most often miss. Thoropass is the only tool here that bundles it: its SOC 2 audit subscription starts at $5,800 a year, so its published starting point for platform plus audit is $14,500. Scytale sells the audit as an add-on at about $4,200 in published guides, and everywhere else the audit is a separate CPA fee quoted by the auditor — so a Vanta or Drata first year is the platform price plus a five-figure audit fee on top.
The medians tell the truer story. Vendr's observed-contract data puts the median annual contract near $20,000 for Vanta and Secureframe, about $25,000 for Drata, about $15,000 for Sprinto and about $30,000 for Thoropass — all well above the entry figures, because most buyers add a framework, a module or a bigger headcount band. The same 25 people and the same SOC 2 cost $7,500 a year at the cheap end and $15,000 at the dear end for the platform alone, and $14,500 to $30,000 once the audit is counted. Budget the median, not the entry price, and get the renewal cap in writing: Sprinto's startup discounts expire by year three, and Thoropass contracts renew with increases of up to 7% a year.
Know the difference: compliance automation vs the audit itself
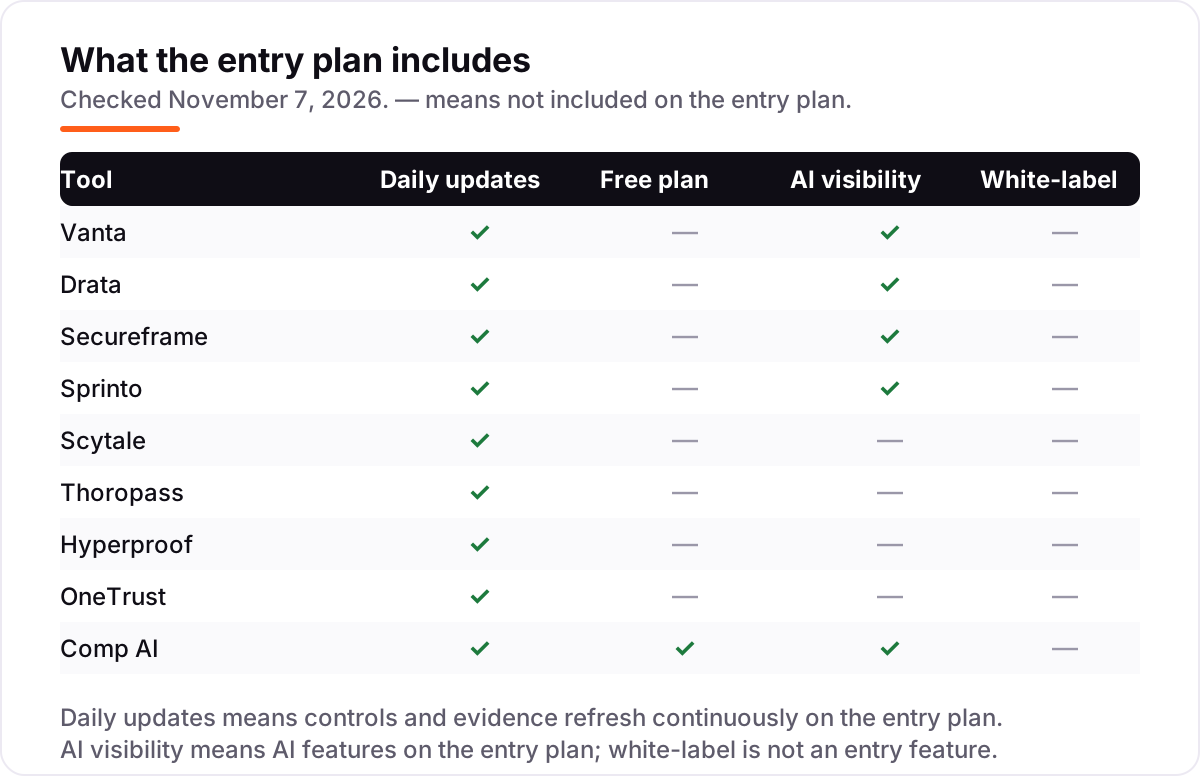
The confusion in this category is between a platform and an attestation. A compliance automation tool collects evidence, monitors controls and prepares the paperwork; it does not issue the SOC 2 report. Only a licensed CPA firm can do that, which is why the audit is a separate purchase on eight of the nine tools in this list. Thoropass is the exception: its affiliated CPA firm performs the audit inside the same workspace, so the platform and the attestation arrive on one contract.
There is a second distinction worth knowing: SOC 2 and ISO 27001 are not the same credential. SOC 2 is an American attestation on security controls, reported over a period for Type II, while ISO 27001 is an international certification of an information security management system. Many SaaS companies pursue both, since enterprise customers ask for each in different markets — and that is exactly when the framework fee matters, because the second credential is priced as an add-on on every tool here.
A third distinction is automation versus a guided service. Tools such as Vanta and Drata automate evidence collection deeply, but they still expect your team to do the remediation work: fixing the control, closing the gap, writing the policy. Tools such as Secureframe, Sprinto and Scytale add a person to the deal — a compliance manager or expert who guides the first audit. Neither model makes a company compliant on its own; the platform shortens the work, but gap closure still needs engineering time and an owner.
Quick comparison: tool type by need
| Buyer | Best pick | Why |
|---|---|---|
| First SOC 2 on the tightest budget | Comp AI | Free self-hosted open-source edition; Sprinto is the cheapest guided option at $9,500/year |
| Most SaaS teams | Vanta | Widest integrations at 400-plus and the largest auditor network, from $14,000/year |
| Engineering-led team | Drata | Custom framework builder and testing-as-code workflows, from $15,000/year |
| Guided first audit | Secureframe | Named compliance manager and a published entry price, from $7,500/year |
| Many frameworks at once | Scytale | 60-plus frameworks with expert support, from $7,500/year; Hyperproof at $12,000/year for mid-market |
| Platform plus audit in one contract | Thoropass | Platform from $8,700/year with the SOC 2 audit from $5,800/year on the same contract |
| Enterprise-wide governance | OneTrust | 50-plus frameworks across privacy, risk and compliance, custom quote |
Mistakes to avoid
- Budgeting on the platform price alone. The audit is a separate fee on eight of the nine tools here. A $7,500 platform plus a five-figure audit is not a $7,500 first year.
- Buying for one framework when customers will ask for two. A second framework costs $2,000 to $7,500 a year extra, so price the year-two framework plan before you sign for year one.
- Ignoring the headcount band. Vanta Essentials covers 1 to 20 employees and Drata Foundation covers 1 to 50 full-time employees; crossing the band means a new quote, not a small uplift.
- Trusting the year-one discount. Sprinto's startup discounts run 60% off in year one and expire by year three, and Thoropass contracts renew with increases of up to 7% a year — model year three before signing.
- Picking enterprise GRC for a first SOC 2. OneTrust is built for large teams with dedicated GRC staff; an early startup will pay for breadth it never uses and spend two months implementing it.
How we chose
We checked each vendor's pricing page and AWS Marketplace listing on November 7, 2026 and recorded the starting price exactly as published, including what it leaves out — the audit, extra frameworks and headcount bands — and we ranked the tools by fit for the most common buyer, a SaaS team preparing for a first SOC 2 audit, not by brand size. Only Secureframe publishes a starting price on its own pricing page; Vanta, Drata, Sprinto, Scytale and Thoropass publish no prices on their own sites, so their figures come from each vendor's own AWS Marketplace listing, and Hyperproof's $12,000 a year is the price Hyperproof supplied to G2 rather than a figure on its own site. Ratings come from G2 review pages checked on November 7, 2026. OneTrust carries no rating here because G2's relevant Tech Risk and Compliance listing was last crawled over three months ago, and the fresh Privacy Automation listing covers a different product. No vendor paid for a place in this list, and none of the links here are affiliate links.
What to do next
Start with the top pick for your situation and run a demo on your real stack: connect your cloud, identity and HR tools, and check whether evidence collects automatically. Confirm the headcount band, the framework count and the audit arrangement in writing before you sign — those three lines decide what you actually pay. If the tools are sorted but new customers are not finding you, our SEO audit service handles the visibility side — or compare providers in our guide to SEO agencies for SaaS companies. Once your tools are in place, find out what's holding your rankings back.
Your stack only works if people find you
SerpAstra fixes what keeps your site off page one and makes it easy for AI assistants to recommend.
Get a free audit→Sources we checked (19)
- Vanta pricing — vanta.com/pricing (checked November 7, 2026)
- Vanta on AWS Marketplace, Essentials $14,000/12 months — aws.amazon.com/marketplace/pp/prodview-5ophamrbfxt44 (checked November 7, 2026)
- Vanta reviews — g2.com/products/vanta/reviews (checked November 7, 2026)
- Drata plans — drata.com/plans (checked November 7, 2026)
- Drata on AWS Marketplace, Foundation $15,000/12 months — aws.amazon.com/marketplace/pp/prodview-3xw4sjqv2pb22 (checked November 7, 2026)
- Drata reviews — g2.com/products/drata/reviews (checked November 7, 2026)
- Secureframe pricing — secureframe.com/pricing (checked November 7, 2026)
- Secureframe reviews — g2.com/products/secureframe/reviews (checked November 7, 2026)
- Sprinto pricing — sprinto.com/pricing (checked November 7, 2026)
- Sprinto reviews — g2.com/products/sprinto-inc/reviews (checked November 7, 2026)
- Scytale pricing — scytale.ai/pricing (checked November 7, 2026)
- Scytale reviews — g2.com/products/scytale-g2/reviews (checked November 7, 2026)
- Thoropass pricing — thoropass.com/pricing (checked November 7, 2026)
- Thoropass reviews — g2.com/products/thoropass/reviews (checked November 7, 2026)
- Hyperproof pricing — hyperproof.com/pricing (checked November 7, 2026)
- Hyperproof reviews and vendor-supplied price — g2.com/products/hyperproof/reviews (checked November 7, 2026)
- OneTrust pricing — onetrust.com/pricing (checked November 7, 2026)
- Comp AI pricing — trycomp.ai/pricing (checked November 7, 2026)
- Comp AI reviews — g2.com/products/comp-ai/reviews (checked November 7, 2026)
Shamim
Founder of SerpAstra
A full-stack SEO and digital marketer who spends most days on Local SEO for dental practices, AI search visibility and lead generation.
Frequently asked questions
What is the best security compliance tool for SaaS companies?
Vanta is the best fit for most SaaS teams: the widest integration net at more than 400 integrations, the largest auditor network, and a Trust Center included, from $14,000 a year. Drata is the better pick for engineering-led teams, and Secureframe for teams that want guided setup.
How much does security compliance software cost for a SaaS company?
Platform prices run from $0 for Comp AI self-hosted to $15,000 a year for Drata Foundation, with most tools starting at $7,500 to $14,000 a year. The audit is a separate fee everywhere except Thoropass, which bundles it, so a first year typically costs $14,500 to $30,000 all in.
Do these tools replace a compliance hire?
No. They replace evidence-chasing, not judgment: scoping, risk decisions and auditor conversations still need an owner. Guided tools such as Secureframe, Sprinto and Scytale let one owner run a program that once needed a team, but no platform makes a company compliant on its own.
What is the difference between SOC 2 and ISO 27001?
SOC 2 is an American attestation on security controls, reported over a period for Type II, while ISO 27001 is an international certification of an information security management system. Many SaaS companies pursue both, since enterprise customers ask for each in different markets.
Can I switch compliance tools later?
Yes, but evidence history and auditor familiarity make switching costly mid-audit. Pick the tool for your year-two framework plan, not just your first audit, and confirm data export before signing. Switching between audits is far cheaper than switching during an observation window.
Is there a free security compliance tool for SaaS?
Comp AI is the only free option here: its core is open source under AGPLv3, so a technical team can self-host it at $0 in licence fees, paying only for hosting and staff time. Its managed hosted plan is quote-only. No other tool in this list offers a free plan.
Free SEO and AI visibility audit
Find out what is holding your rankings back
Send us your site. Within 2 business days you get a written audit, an AI visibility check and a short fix list ranked by impact. Free, with no contract attached.
Request my free audit→Related guides
 Email, SMS & Social MediaBest Email Security Software for 2026: 11 Options Compared by Use CaseCompare the 11 best email security software options for 2026 on price, phishing defense and BEC protection, with every price checked November 6, 2026.Read guide →
 SEO & AI Search8 Best SEO Agencies for SAAS Companies in 20268 best SEO agencies for SaaS companies compared on starting retainer, SaaS focus and AI visibility, with prices checked on the agency's site, November 1, 2026.Read guide →
 SEO & AI SearchBest SEO Audit Software for 2026: 10 Options Compared by Use Case10 best SEO audit software tools compared on price, crawl depth and AI visibility. Prices checked on vendor pricing pages, November 1, 2026.Read guide →