
7 Best Extended Detection Response Software Reviews in 2026, Compared
Best extended detection response software reviews: 7 XDR platforms compared on price, G2 ratings and fit, with 100-endpoint cost example, checked Nov 10, 2026.
 Shamim Mia, Founder, SerpAstraLast verified November 10, 202613 min read
We compare pricing pages, documentation and public reviews. We never accept payment for rankings.
Key takeaways
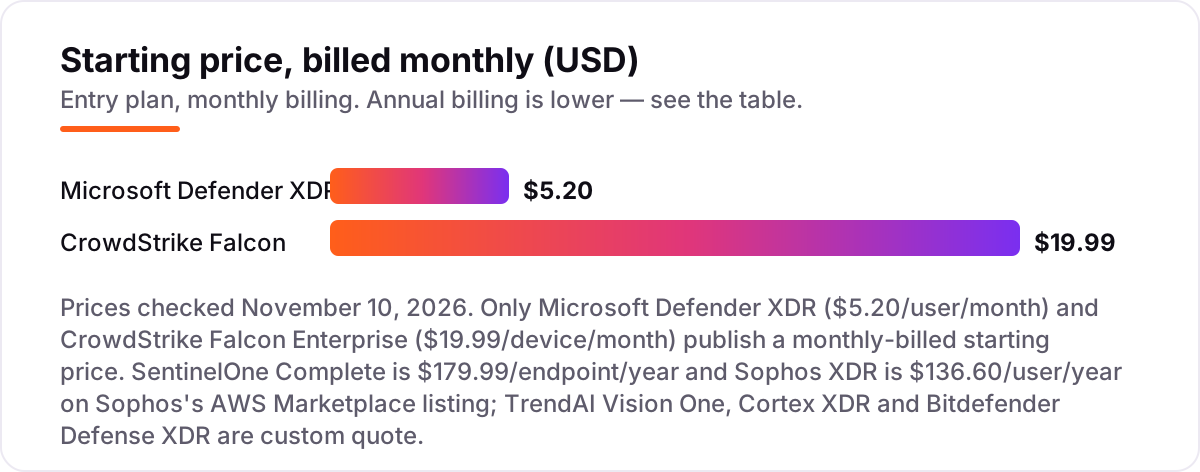
- Microsoft Defender XDR is the best first pick for most teams: $5.20/user/month standalone, or included in Microsoft 365 E5. CrowdStrike Falcon Enterprise is the detection-first pick at $184.99/device/year, and SentinelOne Complete is the published-price alternative at $179.99/endpoint/year.
- Only three of the seven publish a starting price; TrendAI Vision One, Cortex XDR and Bitdefender Defense XDR are quote-only, so budget a sales cycle for those.
- The single most important buying factor is which telemetry sources are included: XDR is only worth the price if it correlates endpoint, identity, email and cloud signals, not just endpoint alerts.
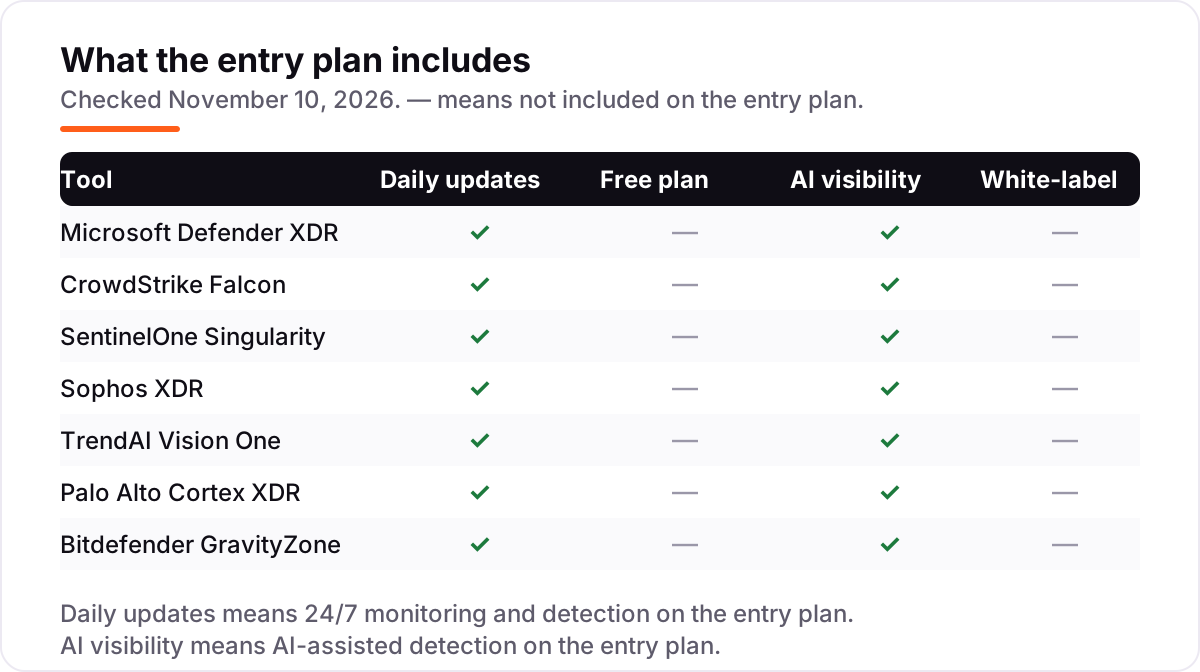
- No tool here has a free plan; every one offers a free trial except Cortex XDR, which is demo-only.
- Every price below was checked on November 10, 2026. Ratings are G2, with review counts shown; Bitdefender shows no rating because no fresh G2 review count was verified.
On this page
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|---|---|---|
| Microsoft Defender XDR | Mid-market IT teams already on Microsoft 365 that want XDR without adding another vendor | $5.20/mo | No (trial) |
| CrowdStrike Falcon | Mid-market security teams that want the strongest detection record and can pay per device | $19.99/mo | No (15-day trial) |
| SentinelOne Singularity | Lean IT teams that want autonomous rollback and a published price with no sales call | $179.99/yr | No (trial) |
| Sophos XDR | Small and mid-market teams running Sophos firewalls that want cross-product XDR telemetry | $136.60/yr | No (30-day trial) |
| TrendAI Vision One | Mid-market and enterprise teams that want endpoint, email, network and cloud in one XDR console | Custom quote | No (30-day trial) |
| Palo Alto Cortex XDR | Enterprise SOC teams already on Palo Alto firewalls that need deep multi-source correlation | Custom quote | No (demo only) |
| Bitdefender GravityZone | Budget-conscious small businesses that want strong protection and XDR as a later add-on | Custom quote | No (30-day trial) |
Make one of these tools?
We re-check this list every quarter. Send a correction, request a review, or ask about a clearly labeled sponsored spot.
Request a listingThe best extended detection response software
Microsoft Defender XDR
Best for: Mid-market IT teams already on Microsoft 365 that want XDR without adding another vendor
Microsoft Defender XDR is the cheapest credible XDR in this list because most buyers already own half of it. The full Defender XDR stack comes inside Microsoft 365 E5, and the endpoint piece alone, Defender for Endpoint Plan 2, costs $5.20 per user per month standalone, with one licence covering up to five devices per user. That makes Defender the default first look.
The catch is that the $5.20 price buys only the endpoint layer. Identity, email and cloud-app signals need E5 at $60 per user per month or the $12 E5 Security add-on on E3, so the real XDR bill is higher than the headline. Reviewers also warn of a steep learning curve and about three months to implement. Buy Defender when your estate is already Microsoft; buy elsewhere when it is not.
What we like
- Full XDR in Microsoft 365 E5 at $60/user/month, or the E5 Security add-on at $12/user/month on E3, so many teams already own most of it
- Correlates endpoint, identity, email and cloud app signals natively, with automated investigation and remediation built in
- One licence covers up to 5 devices per user, so a laptop plus a phone does not cost twice
Watch out for
- The $5.20 standalone price covers only the endpoint piece; identity, email and cloud apps need E5 or add-ons, which pushes the real cost up
- G2 reviewers report a steep learning curve and occasional false positives, and setup takes about 3 months on average
CrowdStrike Falcon
Best for: Mid-market security teams that want the strongest detection record and can pay per device
CrowdStrike Falcon Enterprise is the detection-first pick, and the price is published to the cent: $184.99 per device per year on annual billing, or $19.99 per device per month. That buys Falcon Insight XDR plus OverWatch managed threat hunting, on a single lightweight agent that G2 reviewers praise for detection quality and minimal impact on endpoints. There is no server hardware to run and no sales call needed for the first three tiers.
The honest cost is higher than the headline. Every add-on module costs extra, and reviewers report the bill climbing well past $184.99 once identity protection or extended log retention is added, while servers are priced above the workstation rate. Falcon Complete managed detection is quote-only. Choose CrowdStrike when detection quality matters more than the lowest bill, and price the modules you will actually need before signing.
What we like
- Falcon Enterprise bundles Falcon Insight XDR with 24/7 managed threat hunting (OverWatch) at a published price
- Single lightweight agent with no on-premises servers, and G2 reviewers cite detection quality and minimal endpoint impact most
- Self-serve purchase for Go, Pro and Enterprise with a 15-day free trial and no credit card
Watch out for
- Each add-on module costs extra, and reviewers report the bill climbing well past the headline price once identity protection or extended log retention is added
- Server endpoints are priced higher than workstations, so mixed fleets cost more per endpoint than the headline rate

SentinelOne Singularity
Best for: Lean IT teams that want autonomous rollback and a published price with no sales call
SentinelOne Singularity Complete is the pick for a lean team that wants the agent to act, not just alert. The agent can contain a threat and roll back ransomware damage on the device without waiting for an analyst, which is the feature G2 reviewers mention most. The price is published, $179.99 per endpoint per year, and a 5-to-100-workstation team can budget from the website before talking to anyone.
The limits sit in retention and the channel. Complete keeps 14 days of telemetry, so longer investigations need Commercial at $229.99 per endpoint per year, and every purchase goes through an authorized partner, so the partner's price is the final one. Managed threat hunting is an add-on on Complete. Pick SentinelOne when you want autonomous response and a number up front; pick CrowdStrike when you want hunting included.
What we like
- Agent rolls back ransomware damage on the device without waiting for an analyst, the feature G2 reviewers cite most
- Published per-endpoint prices for Complete and Commercial, so a small team can budget before talking to a partner
- One agent and one console for endpoint and cloud workload protection, with an AI security assistant on Complete
Watch out for
- Complete keeps only 14 days of data; 90-day retention needs Commercial at $229.99/endpoint/year
- Published prices apply to 5-100 workstations and all purchases go through an authorized partner, so the final price is the partner's
- Managed threat hunting is an add-on on Complete, not included

Sophos XDR
Best for: Small and mid-market teams running Sophos firewalls that want cross-product XDR telemetry
Sophos XDR is the value pick for teams that already run Sophos firewalls, because its XDR layer correlates endpoint, firewall, email and cloud signals in one data lake with 90 days of retention. The same agent carries CryptoGuard ransomware rollback and deep-learning malware detection, and a 30-day trial of the XDR tier is available direct from Sophos. For a Sophos shop, the telemetry is already there waiting to be correlated.
The awkward part is pricing. Sophos publishes no price on its own site, so the $136.60 per user per year figure comes from Sophos's own AWS Marketplace listing, and partner quotes vary from there. Servers cost extra, and the G2 evidence is thin at 3.9 out of 5 from only 35 reviews. Buy Sophos XDR when the rest of your estate is already Sophos; otherwise the integration advantage disappears.
What we like
- XDR correlates endpoint, firewall, email and cloud signals in one data lake with 90-day retention for hunting
- CryptoGuard ransomware rollback and deep-learning malware detection in the same agent, with no extra console
- 30-day free trial of Sophos Endpoint Advanced with XDR, direct from Sophos
Watch out for
- Sophos publishes no price on sophos.com; the $136.60 figure comes from its AWS Marketplace listing, and partner quotes vary
- G2's Intercept X listing is thin at 35 reviews and 3.9/5, so the rating is weaker evidence than the others here
- Servers cost extra on top of the per-user price, and the full value needs other Sophos products feeding telemetry

TrendAI Vision One
Best for: Mid-market and enterprise teams that want endpoint, email, network and cloud in one XDR console
TrendAI Vision One, formerly Trend Micro Vision One, is the broadest platform in this list: endpoint, email, network, cloud and risk exposure in one console, with a 30-day free trial needing no credits. Instead of a flat per-seat fee it sells credits, so a team pays for the workload types it actually runs rather than one price for everything.
The trade-off is that nothing is published: no per-unit price, so budgeting needs a sales conversation and the credit maths are hard to compare against per-device rivals. G2 reviewers also note a complex initial setup, with about three months to implement, and flag licensing costs as a concern for smaller teams. Choose Trend when you want one console for the whole estate and can live with a quote; choose a published-price rival when the budget needs a number today.
What we like
- Widest native coverage here: endpoint, email, network, cloud and risk exposure in a single console
- Credit model means you pay for the workload types you actually run instead of a flat per-seat fee
- 30-day free trial with full endpoint security features and no credits needed during the trial
Watch out for
- No published price anywhere, so budgeting needs a sales conversation and the credit maths are hard to compare
- G2 reviewers note the initial setup is complex and takes about 3 months to implement
- Reviewers flag licensing and maintenance costs as a concern for smaller organizations

Palo Alto Cortex XDR
Best for: Enterprise SOC teams already on Palo Alto firewalls that need deep multi-source correlation
Palo Alto Cortex XDR is the enterprise pick, built for SOC teams that already run Palo Alto firewalls. It pulls endpoint, network, cloud and identity data into a single investigation view, includes 90 days of retention by default, and the October 2026 6.0 release adds agentic endpoint security in the same console. When the estate is already Palo Alto, no rival integrates as deeply.
It is also the hardest to buy blind: no published price, no free trial, only a demo, and G2 reviewers call out premium pricing with add-on modules that push costs up fast. Implementation takes about three months, the learning curve is steep, and the agents differ across Windows, Linux and Mac. Buy Cortex XDR when you have a SOC and a Palo Alto estate; a small team without either will find it too much product.
What we like
- Correlates endpoint, network, cloud and identity data into one investigation view, with the strongest Palo Alto firewall integration here
- 90 days of data retention included by default, with 180- and 365-day options available
- Cortex XDR 6.0 (October 2026) adds agentic endpoint security in the same console and sensor
Watch out for
- No published price and no free trial; G2 reviewers call out premium pricing and add-on modules that push the cost up fast
- G2 reviewers report a steep learning curve and a 3-month average implementation
- Windows, Linux and Mac agents differ in features, and reviewers note a performance impact on lower-end systems
Bitdefender GravityZone
Best for: Budget-conscious small businesses that want strong protection and XDR as a later add-on
Bitdefender GravityZone is the budget route into this list, because every tier runs the same detection engine, so the cheapest bundle does not mean weaker protection. Business Security starts from $38 per endpoint per year for small teams, the lowest entry price here, with a 30-day free trial and one cloud console for Windows, macOS, Linux and mobile. For a small business replacing legacy antivirus, that is strong value.
The XDR itself is the catch: Defense XDR is a separate add-on on the top Enterprise tier, so the $38 entry price buys prevention, not detection and response, and the add-on is quote-only. EDR also sits on the higher tiers, and G2 reviewers find the console confusing for new users. Buy GravityZone when budget comes first and XDR can wait; buy a rival when correlation is needed on day one.
What we like
- Same detection engine across every tier, so the cheapest bundle does not mean weaker protection
- Business Security starts from $38/endpoint/year for 3-100 endpoints, the lowest entry price in this list
- 30-day free trial and a single cloud console for Windows, macOS, Linux and mobile
Watch out for
- XDR is a separate Defense XDR add-on on the top Enterprise tier, not included in the entry price
- Enterprise features such as EDR sit on higher tiers, so the entry price buys prevention, not detection and response
- G2 reviewers find the console confusing for new users
These best extended detection response software reviews are for IT and security teams that need one console to catch attacks across endpoints, identity, email and cloud. We ranked seven XDR platforms by fit for a typical mid-market team, checked every published starting price, and marked the three that only sell on quote.
How to choose the best extended detection response software reviews for your team
Start from your estate, not the vendor ranking. XDR is sold three different ways in this list — per user, per device and per credit — so the same 100-person team gets three different bills, and the cheapest headline is not always the cheapest year. Write down how many people, devices and servers you actually protect, then match the billing unit to that count before comparing any price.
- Count people and devices separately. Microsoft and Sophos bill per user, CrowdStrike and SentinelOne bill per device, and Trend bills credits per workload type. A user with a laptop and a phone counts once on per-user pricing and twice on per-device pricing.
- Check which telemetry sources are included. Real XDR correlates endpoint, identity, email, network and cloud signals. If the plan you buy covers endpoints only, you are buying EDR at XDR prices.
- Ask how long telemetry is kept. SentinelOne Complete keeps 14 days and Commercial keeps 90; Cortex XDR and Sophos XDR include 90 days by default. Short retention means an investigation that starts late has nothing to look at.
- Decide self-managed or managed. Falcon Complete, Defender Experts and Sophos MDR put vendor analysts on your alerts, and they are priced separately from the platform. A small team with no SOC should price the managed option, not just the licence.
- Watch the server rate. Servers are priced above workstations at CrowdStrike and Sophos, so a fleet with many servers costs more per endpoint than the headline rate suggests.
- Run the trial on your own fleet. Every tool here except Cortex XDR offers a free trial. Deploy it on a real slice of machines, trigger a test detection, and time how long the investigation takes before you sign.
XDR pricing: what you will actually pay
Take a team of 100 people with 100 laptops and 20 servers. On Microsoft Defender for Endpoint Plan 2 standalone, 100 users at $5.20 a month is $6,240 a year — but that buys only the endpoint layer. The full XDR stack needs Microsoft 365 E5 at $60 per user per month, which is $72,000 a year for 100 users, or E3 at $39 plus the $12 E5 Security add-on, which is $61,200 a year. The E5 routes cost far more because they include the whole Microsoft 365 productivity suite, not just security, so compare them on that basis, not as a security-only price.
On CrowdStrike Falcon Enterprise, 100 devices at $184.99 a year is $18,499 on annual billing, or $23,988 if you pay $19.99 per device per month instead. The 20 servers sit on top of that at a higher per-device rate, and any identity or log-retention module adds more. On SentinelOne Complete, 100 endpoints at $179.99 a year is $17,999, and that price fits exactly inside the published 5-to-100-workstation scope. On Sophos XDR, 100 users at $136.60 a year is $13,660 on the AWS Marketplace listing, before server uplifts and partner discounts. TrendAI Vision One, Cortex XDR and Bitdefender Defense XDR publish no number at all, so there is no honest figure to put in this example — get the quote before you budget.
The lesson is the billing unit, not the headline. Microsoft looks cheapest at $5.20, but the comparable full-XDR route is the $12 add-on or E5, while CrowdStrike and SentinelOne look close at $184.99 against $179.99 until servers and modules are added. Price every option at your real mix of users, devices and servers, and leave room for the retention and module add-ons you will want in year two. If the rollout drives traffic to your site, check those pages with our free title tag checker so the visits land on pages worth reading. And once you have the XDR bill mapped, the same discipline helps elsewhere: our SEO audit service reviews what a business already pays for before it buys more.
XDR vs EDR vs MDR: know the difference
The three letters get mixed up in sales calls, and the mix-up costs money. EDR, endpoint detection and response, watches endpoints only: it detects and responds to threats on laptops, desktops and servers. XDR, extended detection and response, takes the EDR feed and correlates it with identity, email, network and cloud signals, so one incident shows the whole attack — the phished login, the odd sign-in, the malware on the laptop — instead of three separate alerts in three consoles. MDR, managed detection and response, is not a product at all: it is a service where the vendor's analysts watch the alerts for you, usually built on top of an EDR or XDR platform.
That is why the tiers matter. CrowdStrike Falcon Go at $59.99 per device per year is endpoint protection, not XDR; the XDR layer, Falcon Insight, starts at Falcon Enterprise. Microsoft Defender for Endpoint Plan 2 is the EDR piece, and Defender XDR is the correlation layer on top of it plus Defender for Identity, Office 365 and Cloud Apps. Buying the cheaper tier and expecting XDR is the most common mistake in this category.
The managed side needs the same care. Falcon Complete, Microsoft Defender Experts and Sophos MDR are MDR services with their own quotes, and they sit on top of the platform licence rather than replacing it. A small team with no security staff should budget for the service, not just the software, because an XDR console nobody watches is just an expensive alert feed. If you have an analyst who can work the queue daily, the self-managed platform is enough; if you do not, the managed service is the real product you are buying.
Quick comparison: tool type by need
| Buyer | Best pick | Why |
|---|---|---|
| Already on Microsoft 365 | Microsoft Defender XDR | $5.20/user/month standalone, or $0 extra inside E5 |
| Strongest detection, budget allows | CrowdStrike Falcon | Published $184.99/device/year, lightweight agent |
| Lean team, no sales call | SentinelOne Singularity | Published $179.99/endpoint/year, autonomous rollback |
| Sophos firewall shop | Sophos XDR | $136.60/user/year via AWS Marketplace, 90-day retention |
| Broadest platform, one console | TrendAI Vision One | Quote-only, credit-based, 30-day trial |
| Palo Alto shop with a SOC | Palo Alto Cortex XDR | Quote-only, 90-day retention included, demo only |
| Tightest budget, strong engine | Bitdefender GravityZone | Defense XDR quote-only; entry tier from $38/endpoint/year |
How we chose
We ranked the tools by fit for the most common buyer, a mid-market IT team with a small security staff and roughly 100 endpoints, not by brand size. Prices were checked on November 10, 2026: CrowdStrike and SentinelOne publish theirs on their own pricing pages, and SentinelOne's page renders its prices by script, so we cross-checked the $179.99 and $229.99 figures against several independent reads of the same page from October and November 2026. Microsoft publishes no standalone Plan 2 price on a public page, so the $5.20 figure is from Microsoft's October 2026 price list as reported by licensing trackers, and the E5 and add-on figures come from the same price list. Sophos publishes no price on its own site, so the $136.60 figure comes from Sophos's own AWS Marketplace listing and is disclosed as such, not presented as a vendor-page price. TrendAI Vision One, Cortex XDR and Bitdefender Defense XDR publish no price, so we show custom quote and used no third-party price for them, including the $12/user/month and $1,000-a-year figures that circulate in directories. Ratings come from G2 pages crawled within the last few days, except Bitdefender, where no fresh verified G2 count was found, so it shows no rating rather than an estimate. G2 also carries a larger Sophos Endpoint listing at 4.7 out of 5 from 825 reviews; we used the Intercept X listing because that is the named product, and its small base is disclosed in the card. No vendor paid for a place in this list, and none of the links here are affiliate links.
What to do next
Start with the decision path above: count your people, devices and servers, check which telemetry sources each plan includes, and ask about retention before you compare prices. Then take the free trial of your top pick — every tool here except Cortex XDR offers one — and run it on a real slice of your fleet for two weeks, timing a test investigation end to end. If the console makes sense to the person who will actually work the queue, you have your tool. Once your tools are in place, find out what's holding your rankings back.
Your stack only works if people find you
SerpAstra fixes what keeps your site off page one and makes it easy for AI assistants to recommend.
Get a free audit→Sources we checked (15)
- Microsoft Defender for Endpoint Plan 2 pricing, $5.20/user/month — Microsoft October 2026 price list, via Redress Compliance (checked November 10, 2026)
- Microsoft 365 E5 $60/user/month and E5 Security add-on $12/user/month — CyberMark Agency XDR pricing (checked November 10, 2026)
- Microsoft Defender XDR on G2 — 4.5/5, 289 reviews (checked November 10, 2026)
- CrowdStrike Falcon pricing — crowdstrike.com/en-us/pricing (checked November 10, 2026)
- CrowdStrike Falcon on G2 — 4.7/5, 682 reviews (checked November 10, 2026)
- SentinelOne platform pricing — sentinelone.com/platform-packages (checked November 10, 2026)
- SentinelOne Singularity on G2 — 4.7/5, 212 reviews (checked November 10, 2026)
- Sophos XDR pricing, $136.60/user/year on AWS Marketplace — Endpoint Index Sophos pricing (checked November 10, 2026)
- Sophos Intercept X on G2 — 3.9/5, 35 reviews (checked November 10, 2026)
- Trend Vision One publishes no pricing — Heimdal Security CrowdStrike vs Trend Micro (checked November 10, 2026)
- TrendAI Vision One on G2 — 4.7/5, 252 reviews (checked November 10, 2026)
- Cortex XDR pricing, quote-only — G2 Cortex XDR pricing page (checked November 10, 2026)
- Cortex XDR on G2 — 4.5/5, 94 reviews (checked November 10, 2026)
- Bitdefender GravityZone entry pricing, from $38/endpoint/year — Endpoint Index SMB price index (checked November 10, 2026)
- Bitdefender Defense XDR is an add-on to Business Security Enterprise — iFeelTech GravityZone review (checked November 10, 2026)
Shamim
Founder of SerpAstra
A full-stack SEO and digital marketer who spends most days on Local SEO for dental practices, AI search visibility and lead generation.
Frequently asked questions
What is the best extended detection response software in 2026?
For most teams, Microsoft Defender XDR: it costs $5.20/user/month standalone or comes inside Microsoft 365 E5, and it correlates endpoint, identity, email and cloud signals natively. CrowdStrike Falcon Enterprise is the detection-first pick at $184.99/device/year, and SentinelOne Complete is the best published-price alternative at $179.99/endpoint/year with autonomous rollback.
How much does XDR software cost?
Published starting prices run from $5.20/user/month for Microsoft Defender for Endpoint Plan 2 to $19.99/device/month for CrowdStrike Falcon Enterprise. SentinelOne Complete is $179.99/endpoint/year and Sophos XDR is $136.60/user/year. TrendAI Vision One, Cortex XDR and Bitdefender Defense XDR are quote-only, so their cost depends on a sales conversation.
Is there a free XDR tool?
No tool in this list has a permanent free plan. Six of the seven offer a free trial: CrowdStrike for 15 days, Sophos, TrendAI Vision One and Bitdefender for 30 days, and Microsoft and SentinelOne offer trials with no stated length. Cortex XDR is the exception, with a demo only and no free trial.
What is the difference between XDR and EDR?
EDR watches endpoints only: it detects and responds to threats on laptops, desktops and servers. XDR correlates signals from endpoints plus identity, email, network and cloud apps into one incident, so an analyst sees the whole attack instead of one alert at a time. Every tool in this list is XDR, but the cheaper tiers of some, such as CrowdStrike Go, are endpoint-only.
What is the difference between XDR and MDR?
XDR is software: a platform that correlates signals and automates response. MDR is a managed service: people watching the alerts for you, usually built on top of an EDR or XDR platform. CrowdStrike Falcon Complete, Microsoft Defender Experts and Sophos MDR are MDR services, not products, and they cost extra on top of the platform licence.
Can I buy XDR software without talking to sales?
Partly. CrowdStrike sells Falcon Go, Pro and Enterprise self-serve from its pricing page, and Microsoft sells Defender for Endpoint Plan 2 standalone. SentinelOne publishes prices but sells through authorized partners. TrendAI Vision One, Cortex XDR and Bitdefender Defense XDR are quote-only, so those three always need a sales conversation.
What should I check before paying for XDR?
Four things: which telemetry sources are included on the plan you are buying, how long data is kept (14 days on SentinelOne Complete, 90 days on Cortex XDR and Sophos XDR), whether servers cost more than workstations, and whether the price is per user or per device. A user with a laptop and a phone counts once on per-user pricing and twice on per-device pricing.
Free SEO and AI visibility audit
Find out what is holding your rankings back
Send us your site. Within 2 business days you get a written audit, an AI visibility check and a short fix list ranked by impact. Free, with no contract attached.
Request my free audit→Related guides
 IT, Security & DevOps9 Best MDR Software for Small Business Security in 2026, ComparedCompare the 9 best mdr software for small business security options on price, 24/7 SOC cover and free trials, with every price checked November 7, 2026.Read guide →
 IT, Security & DevOps12 Best Security Software for Small Business in 2026, ComparedCompare the 12 best security software for small business options on price, endpoint protection and passwords, with prices checked November 7, 2026.Read guide →
 IT, Security & DevOpsBest Antivirus Software Review for 2026: 10 Options Compared by Use CaseCompare the best antivirus software review picks for 2026: 10 suites with prices, renewal costs, free plans and device limits, checked November 6, 2026.Read guide →