
9 Best MDR Software for Small Business Security in 2026, Compared
Compare the 9 best mdr software for small business security options on price, 24/7 SOC cover and free trials, with every price checked November 7, 2026.
 Shamim Mia, Founder, SerpAstraLast verified November 7, 202614 min read
We compare pricing pages, documentation and public reviews. We never accept payment for rankings.
Key takeaways
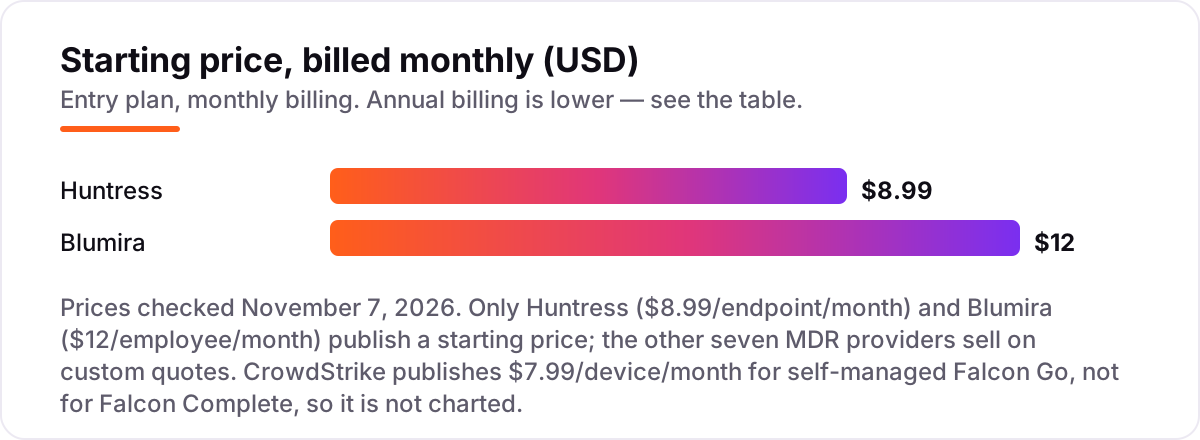
- Huntress is the cheapest published MDR here at $8.99/endpoint/month, Blumira follows at $12/employee/month, and the other seven providers sell on custom quotes — so get at least two quotes before you sign.
- The single most important buying factor is the billing unit: per endpoint, per employee and per user produce wildly different bills for the same company, so price every shortlist option at your real headcount.
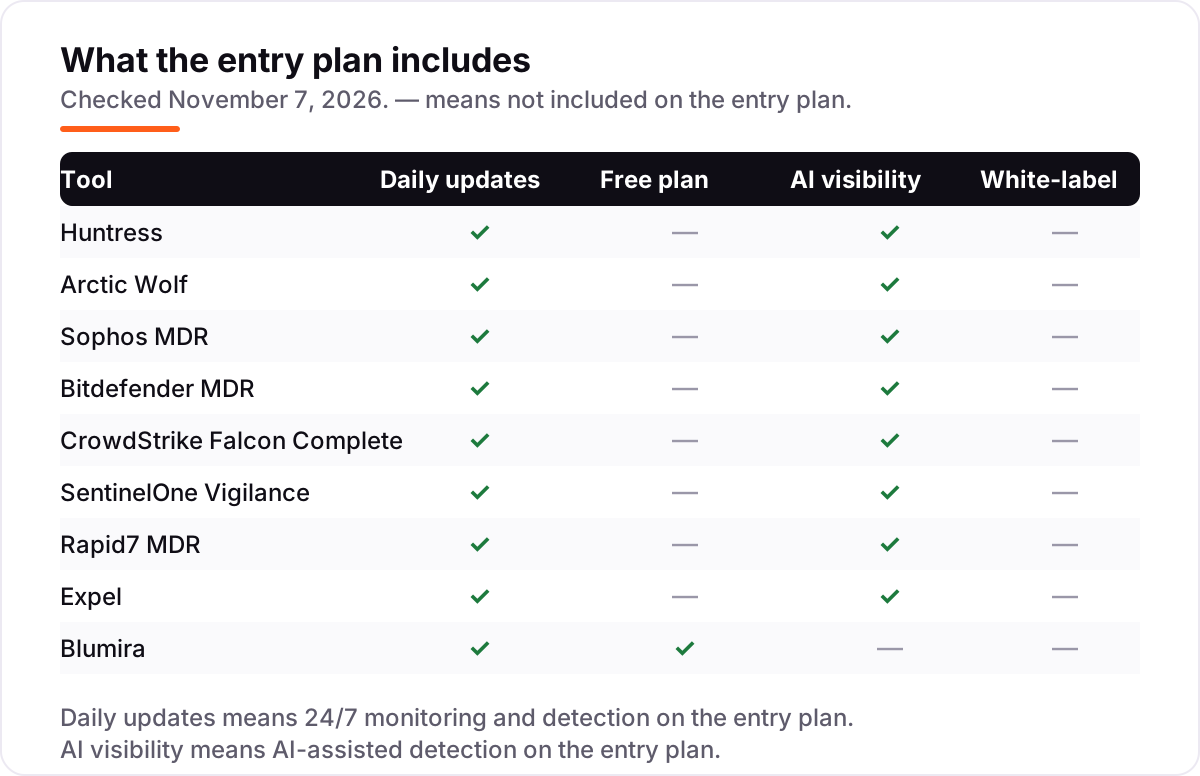
- No MDR in this list has a free plan except Blumira's free SIEM edition — the rest offer trials or nothing at all, so budget for a paid service from day one.
- MDR is a managed service, not software you run yourself: the 24/7 analysts are the product, and the cheapest way to buy them is usually through an MSP partner.
On this page
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|---|---|---|
| Huntress | Small businesses with no security staff that want a 24/7 human SOC watching every endpoint | $8.99/endpoint/mo | No (free trial) |
| Arctic Wolf | Small businesses that want flat, predictable security-operations pricing with no per-alert fees | Custom quote | No |
| Sophos MDR | Businesses already running Sophos Intercept X, Firewall or Email that want the vendor's own analysts on watch | Custom quote | No |
| Bitdefender MDR | Small businesses that want top-rated prevention with a managed response team on top | Custom quote | No |
| CrowdStrike Falcon Complete | Businesses that want the Falcon platform fully managed by CrowdStrike's own team | Custom quote | No (free trial) |
| SentinelOne Vigilance | SentinelOne customers adding 24/7 human threat hunting to the Singularity platform | Custom quote | No |
| Rapid7 MDR | Companies that want MDR plus unlimited incident response on the tools they already own | Custom quote | No |
| Expel | Teams that want a SOC operating the EDR, SIEM and cloud tools they already have | Custom quote | No |
| Blumira | Small IT teams that want flat per-employee pricing with a year of log retention included | $12/employee/mo | Yes (free SIEM) |
Make one of these tools?
We re-check this list every quarter. Send a correction, request a review, or ask about a clearly labeled sponsored spot.
Request a listingThe best mdr software for small business security
Huntress
Best for: Small businesses with no security staff that want a 24/7 human SOC watching every endpoint
Huntress is the small-business answer to the MDR price problem: it publishes its price, and the 24/7 human SOC is included in it. Managed EDR costs $8.99 per endpoint per month at 50 to 99 endpoints, dropping to $7.99 at 100, with no setup or onboarding fees and a 12-month term. The SOC investigates every alert and stages remediations, so a company with no security staff gets a night shift it could never hire.
The catch is the buying shape. Purchase needs a 50-endpoint minimum, so a 10-person firm buys through an MSP partner, and identity, SIEM and training are separate per-unit products that stack on top of EDR. Buy Huntress when you want a published price and a SOC at small-business scale; buy Arctic Wolf or Blumira when the per-endpoint minimum or the add-on stack does not fit.
What we like
- The only MDR here with a published per-endpoint price, and the 24/7 SOC is included at no extra cost
- Built for small businesses and the MSPs that serve them, with deployment in minutes per endpoint
- Human analysts investigate and remediate threats, not just send alerts
- Per-unit pricing for EDR, identity, SIEM and training, so you buy only the coverage you need
Watch out for
- Direct purchase needs a 50-endpoint minimum and a 12-month term — smaller firms buy through an MSP
- Identity, SIEM and training are separate per-unit products, so the full stack costs more than EDR alone
- No published price for the managed SIEM or ITDR add-ons beyond the per-unit list rates
Arctic Wolf
Best for: Small businesses that want flat, predictable security-operations pricing with no per-alert fees
Arctic Wolf sells security operations as a service, and its pitch is the one small businesses understand fastest: a flat rate, with no metering by alerts, tokens or data volume. The Aurora platform watches endpoints, networks, cloud and identity around the clock, and a named Concierge Security Team acts as your security contact instead of a ticket queue. More than 10,000 customers buy it, many through MSP partners.
The trade-off is the buying motion. There is no published price to compare before you engage, so budgeting starts with a scoping call, and onboarding a broad platform takes longer than deploying a single-product MDR. Buy Arctic Wolf when budget predictability is your top criterion and you want one vendor watching everything; buy Huntress when you want a published per-endpoint price first.
What we like
- Flat, predictable pricing with no token metering and no per-alert fees
- Covers endpoints, network, cloud and identity from one platform with 24/7 monitoring
- Concierge Security Team gives every customer a named security contact
- Large MSP and channel network, so small businesses can buy through a local partner
Watch out for
- Quote-based pricing still needs a sales process, so there is no price to compare before you engage
- Broad platform scope means onboarding takes longer than a single-product MDR
- Smallest buyers usually engage through an MSP partner rather than direct

Sophos MDR
Best for: Businesses already running Sophos Intercept X, Firewall or Email that want the vendor's own analysts on watch
Sophos MDR puts the vendor's own analysts on your Sophos-protected environment around the clock. Because the team works with Sophos endpoint, firewall and email telemetry natively, detection and response avoid the integration gaps that plague multi-vendor setups. Reviewers rate it 4.7 out of 5 on G2 across 709 reviews, praising fast threat detection and the way it cuts alert fatigue for small IT teams.
The logic is ecosystem: if you already run Sophos Intercept X and Sophos Firewall, adding MDR is the cheapest path to 24/7 coverage, and the complete response tier lets analysts contain threats on your behalf. If you run someone else's endpoint, the case weakens considerably. Buy Sophos MDR when you are standardizing on Sophos; compare Huntress or Arctic Wolf when you are not.
What we like
- The MDR team works natively with Sophos endpoint, firewall and email telemetry, so there are no integration gaps
- 24/7 expert monitoring with threat hunting and rapid response, rated 4.7/5 on G2 across 709 reviews
- Gartner Peer Insights Customers' Choice recognition across endpoint, firewall and MDR
- Two service tiers, including a complete response option where analysts act on your behalf
Watch out for
- Best value is locked inside the Sophos ecosystem — the case weakens on another vendor's endpoint
- Quote-only pricing means no number to compare until you go through sales or a partner
- Reviewers note the service can be costly for the smallest organizations
Bitdefender MDR
Best for: Small businesses that want top-rated prevention with a managed response team on top
Bitdefender's argument is prevention first: its engines consistently rank at the top of independent tests, which means fewer incidents reach the response stage at all. The MDR service layers 24/7 monitoring and response over the GravityZone platform, covering endpoints, cloud workloads and email, and it bolts onto the same console businesses already use for Bitdefender endpoint protection.
The friction is the buying motion. Bitdefender's small-business products are famously easy to buy online; the MDR service is not, running through quotes and partners instead. Businesses already on GravityZone should ask their partner for the MDR add-on price. Businesses choosing fresh should weigh prevention-plus-MDR from one vendor against best-of-breed detection with a separate SOC.
What we like
- Prevention-first engine that consistently ranks at the top of independent tests, so fewer incidents reach the SOC
- 24/7 monitoring and response layered over the GravityZone platform, covering endpoints, cloud and email
- Strong fit for businesses already running GravityZone — the MDR service bolts onto the same console
- Suits the 50-to-200-user band where small businesses usually buy MDR, according to partner reviews
Watch out for
- MDR is sold through quotes and partners, not bought online like Bitdefender's small-business products
- No published MDR price, so budgeting needs a partner quote first
- Only six G2 reviews cover the MDR service itself, so review evidence is thin
CrowdStrike Falcon Complete
Best for: Businesses that want the Falcon platform fully managed by CrowdStrike's own team
Falcon Complete is CrowdStrike's MDR tier: the full Falcon platform with CrowdStrike's own team doing the monitoring, hunting and response around the clock, backed by a breach prevention warranty of up to $1 million. It is the most turnkey way to get elite endpoint protection without hiring anyone, and the single lightweight agent covers endpoints, identity and cloud workloads.
The honest math for small business is that Complete is priced like the premium product it is, and many companies under 200 employees get better value from Falcon Go or Pro paired with an MSP that provides the human layer. Falcon Go publishes at $59.99 per device per year, capped at 100 devices. Buy Complete when you want CrowdStrike's team specifically and can justify the premium.
What we like
- Elite detection on the Falcon platform with a breach prevention warranty up to $1 million
- 24/7 expert-led monitoring, hunting and response from CrowdStrike's own team
- Self-managed bundles publish prices, so Falcon Go at $7.99/device/month is a real on-ramp
- Single lightweight agent covers endpoints, identity and cloud workloads
Watch out for
- Falcon Complete is priced like the premium product it is — many small firms get better value from Falcon Go or Pro plus a partner
- No published price for the managed tier; the $7.99 figure covers self-managed Falcon Go only
- The 2024 faulty content update is a fair due-diligence topic: ask about staged rollouts and rollback

SentinelOne Vigilance
Best for: SentinelOne customers adding 24/7 human threat hunting to the Singularity platform
SentinelOne's Singularity platform is known for autonomous detection and one-click remediation, and Vigilance is the managed layer on top: 24/7 monitoring, threat hunting and response from SentinelOne's SOC. The company has been named a Leader in Gartner's endpoint protection Magic Quadrant six years running, which is why it shows up on every serious shortlist.
For small business, Vigilance almost always arrives through a partner or MSP rather than direct, which is fine: the partner handles onboarding and the day-to-day relationship. The platform's depth is more than a 30-person company needs, but that is not a drawback in practice since you only use what you buy. Compare the partner's all-in price against Huntress and Arctic Wolf before signing.
What we like
- AI-native Singularity platform with autonomous detection and one-click remediation
- Vigilance adds 24/7 human threat hunting and response on top of the autonomous platform
- Six-year Gartner Magic Quadrant Leader for endpoint protection
- Fast-responding Vigilance team, praised in the small review base for clear remediation steps
Watch out for
- Quote-based and usually partner-delivered, so small businesses buy through a channel, not direct
- Only six G2 reviews cover Vigilance Respond itself, so review evidence is thin
- Platform depth — identity, cloud and data — exceeds what a small IT team will use

Rapid7 MDR
Best for: Companies that want MDR plus unlimited incident response on the tools they already own
Rapid7's MDR stands out on one line: unlimited incident response is included. Most MDR providers meter or cap IR hours; Rapid7's bundled approach means a bad month does not become a second invoice. The service runs on its Insight platform with 24/7 monitoring, detection and remediation, and its open XDR approach ingests telemetry from tools you already own rather than demanding rip-and-replace.
Rapid7's center of gravity is the mid-market rather than the very small business, so companies under 100 employees typically engage through a partner. The platform's breadth can complicate a simple MDR evaluation, so focus the demo on the MDR service specifically. For businesses that already run Rapid7 products, the MDR attach is the natural next step.
What we like
- Unlimited incident response is bundled — a bad month does not become a second invoice
- Open XDR approach ingests telemetry from tools you already own instead of demanding rip-and-replace
- 24/7 monitoring, detection and remediation on the Insight platform
- Natural next step for businesses already running Rapid7 products
Watch out for
- Mid-market focus means the smallest businesses usually engage through a partner
- Platform breadth — vulnerability management, cloud security, SIEM — adds evaluation complexity
- Only ten G2 reviews cover the MDR service, so review evidence is thin
Expel
Best for: Teams that want a SOC operating the EDR, SIEM and cloud tools they already have
Expel takes the opposite approach from the platform vendors: keep the EDR, SIEM and cloud tools you already have, and Expel's SOC operates them for you. Analysts triage alerts, investigate and remediate across your stack, and every investigation is visible to you, which answers the trust question most MDR buyers quietly have. The company is a Forrester Wave Leader in MDR services with strong marks for transparency.
The catch is arithmetic: Expel's fee sits on top of whatever you pay for the underlying tools, so the all-in cost can exceed a bundled platform. It makes most sense for teams that already own good tools and want humans to run them, rather than for companies buying their first endpoint product. Get the all-in number in writing before you compare it with Huntress or Arctic Wolf.
What we like
- Keeps the EDR, SIEM and cloud tools you already have — Expel's SOC operates them for you
- Every investigation is visible to you, which answers the trust question most MDR buyers have
- Forrester Wave Leader in MDR services with strong marks for transparency
- Analysts triage, investigate and remediate across your whole stack, not just one agent
Watch out for
- Expel's fee sits on top of what you already pay for the underlying tools, so the all-in cost can exceed a bundle
- Premium-priced for what it is — reviewers flag cost as the main trade-off
- No free plan and no published price, so every evaluation starts with a sales conversation

Blumira
Best for: Small IT teams that want flat per-employee pricing with a year of log retention included
Blumira prices the way small IT teams wish every security vendor priced: per employee, not per gigabyte. Detect starts at $12 per employee per month, Respond at $16 adds the endpoint agent and 24/7 incident support, and Automate at $21 adds AI-assisted investigation and automated containment. Every edition includes a year of unlimited log retention, which removes the retention anxiety that plagues SIEM budgeting.
The catch is the employee-count model. Pricing is based on knowledge workers — staff with a corporate email and workstation — so headcount audits matter at renewal, and contractors can inflate the bill. The free SIEM edition is a genuine starting point, though. Buy Blumira when you want flat-rate security operations and already live in Microsoft 365 or Google Workspace.
What we like
- Flat per-employee pricing with no data-volume charges, so costs stay predictable as log volume grows
- Every edition includes a year of unlimited log retention
- SIEM, XDR and EDR in one platform, with a free SIEM edition to start on
- Highest ease-of-setup scores in this list, praised by reviewers for a fast start
Watch out for
- Pricing counts every knowledge worker, so contractors and part-timers inflate the headcount at renewal
- AI-assisted investigation and automated containment wait for Automate at $21/employee/month
- Onboarding costs $250 on Detect and $500 on Respond — only Automate includes it
A small business gets attacked like an enterprise but defends like a small business: no SOC, no night shift, maybe one IT person who also resets passwords. The best mdr software for small business security closes that gap by renting you a security operations center — human analysts watching your endpoints around the clock, investigating alerts and containing threats before they become incidents. We ranked the nine providers below by fit for the most common buyer, a company of 10 to 100 people with no dedicated security staff, and every price was checked on November 7, 2026.
How to choose the best mdr software for small business security
- Start with the billing unit. Huntress charges per endpoint, Blumira per employee, and the rest quote per user, device or environment — so price every shortlist option at your real headcount, not at the headline rate.
- Check who actually watches at 3 a.m. Every tool here claims 24/7 coverage, but ask whether analysts investigate and contain threats or only send alerts. Huntress, Arctic Wolf and CrowdStrike Complete all include human-led response; a tool that only alerts you is EDR, not MDR.
- Count the minimums before you fall in love. Huntress needs 50 endpoints on a direct purchase, CrowdStrike Falcon Go caps at 100 devices, and Blumira counts every knowledge worker. A minimum that does not fit your size means buying through a partner.
- Ask what sits outside the quote. Onboarding, incident response hours and extra products stack on top: Rapid7 bundles unlimited incident response, while Blumira charges $250–$500 for onboarding on its cheaper editions.
- Match the service to the stack you already own. Sophos MDR and Bitdefender MDR are strongest inside their own ecosystems; Expel and Rapid7 are strongest when you already own the underlying tools.
Security is one system in your stack, not the whole stack. If the business also needs to be found online, our guide to email security software covers the inbox side of the same problem, and our antivirus software review compares the self-managed alternative for firms that are not ready for a SOC. And before you publish new pages for the services you sell, run your titles through the free SERP snippet preview tool — it shows exactly how the title and description will look in Google.
Whatever you shortlist, trial it with real endpoints before you pay. The free trials in this list are long enough to run one genuine week — your devices, your users, your alerts — and that week tells you more than any review can. Check two things in the trial: that alerts reach a human who acts on them without you chasing, and that the console shows you what the SOC did. Every provider here should be able to show you both before you sign a 12-month term.
MDR software for small business security pricing: what you will actually pay
Take a 50-person business with 50 endpoints. On published list prices, Huntress Managed EDR costs 50 × $8.99, or $449.50 a month — $5,394 a year on the 12-month term. Blumira Detect costs 50 × $12, or $600 a month — $7,200 a year — and Respond, the edition with 24/7 incident support, costs 50 × $16, or $800 a month and $9,600 a year. Those are the only two all-in MDR numbers in this list that you can compute without a sales call.
The other seven providers need a scoped quote, so treat the Huntress figure as the floor: any quote far above $5,394 a year for the same 50 endpoints should come with a clear reason, such as broader coverage or a dedicated analyst. For scale, CrowdStrike's self-managed Falcon Go costs 50 × $59.99 a year, or $2,999.50 — cheaper, but it is antivirus without a SOC, so it is not the same purchase. A quote-only MDR that costs less than the self-managed bundle should make you suspicious, not happy.
Three costs sit outside every number above. First, onboarding: Blumira charges $250 on Detect and $500 on Respond, and Huntress states there are no setup fees. Second, the add-ons: Huntress prices identity, SIEM and training per unit on top of EDR, so the full stack costs more than $449.50 a month. Third, incident response: Rapid7 bundles unlimited incident response, while other providers meter it or cap the hours. If you run a business that cannot afford downtime, ask every vendor to put the incident-response terms in writing before you compare prices.
Know the difference: MDR vs EDR vs MSSP
The confusion in this category is between three things that sound alike. EDR is software: an agent on each endpoint that detects suspicious behavior and can isolate a machine, which your own team must watch and operate. MDR is a managed service: the vendor's analysts watch the EDR around the clock, investigate alerts and contain threats for you — the humans are the product. An MSSP is broader still: an outside firm that runs some or all of your security operations, often across many tools and sometimes on-site, under a custom contract.
The practical test is the 3 a.m. question. With EDR alone, an alert at 3 a.m. waits for your IT person to wake up. With MDR, an analyst investigates it at 3 a.m. and contains it. With an MSSP, someone may also be patching your servers and writing your compliance reports. Small businesses usually need MDR: EDR without a night shift leaves alerts unread, and a full MSSP is more than a 50-person company needs or can afford.
There is a second, quieter confusion: a SOC and a helpdesk are not the same thing. A helpdesk resets passwords and fixes printers; a SOC hunts threats. When a vendor says "24/7 support," ask whether that means analysts watching for intrusions or agents answering the phone. The providers in this list all run real SOCs — that is what the "managed" in MDR means — but the distinction matters when you compare them against cheaper tools that only offer round-the-clock support lines.
Quick comparison: tool type by need
| Buyer | Best pick | Why |
|---|---|---|
| Small business, no security staff | Huntress | Published $8.99/endpoint/month with the 24/7 SOC included |
| Budget predictability matters most | Arctic Wolf | Flat-rate pricing with no per-alert fees, custom quote |
| Already running Sophos | Sophos MDR | Vendor analysts on your own Sophos stack, custom quote |
| Already running Bitdefender | Bitdefender MDR | Top-rated prevention plus managed response, custom quote |
| Want the Falcon platform managed | CrowdStrike Falcon Complete | CrowdStrike's own team plus a breach warranty, custom quote |
| Want a free starting tier | Blumira | Free SIEM edition, paid editions from $12/employee/month |
Mistakes to avoid
- Comparing a per-endpoint price with a per-employee price. Huntress at $8.99 per endpoint and Blumira at $12 per employee are not the same bill for the same company. Convert every option to your real endpoint and headcount numbers before you rank them.
- Buying EDR when you need MDR. A self-managed bundle like Falcon Go is cheaper, but nobody watches it at night. If no one on your team reads alerts after hours, the managed service is the purchase, not the software.
- Budgeting on the entry product, then finding the SOC costs extra. Huntress's identity, SIEM and training products are separate per-unit charges, and Expel's fee sits on top of the tools you already own. Price the whole stack, not the first line.
- Ignoring the minimums. A 50-endpoint direct minimum or a 100-device cap changes who you can buy from. Check the minimum before the demo, or you will waste a week evaluating a tool you cannot buy direct.
- Signing before you see an investigation. Ask each vendor to walk you through a real investigation report from a customer like you. If they cannot show you what the SOC actually does, you are buying a promise, not a service.
How we chose
We checked each vendor's own pricing page on November 7, 2026 and recorded the starting price exactly as shown: only Huntress and Blumira publish one, and the other seven sell on custom quotes, which we record as such rather than estimating. Direct page access failed on the check date, so the two published prices were verified against fresh search-index copies of the vendors' own pricing pages, crawled within the last few days and corroborated by independent October–November 2026 reads. Ratings come from fresh G2 crawls of the exact product pages, except Bitdefender MDR, whose G2 listing holds only six reviews and had not been crawled for 15 days, so we show no rating for it rather than a stale one. The CrowdStrike rating is for the Falcon Endpoint Protection Platform listing on G2, which covers Falcon Complete as an edition. No vendor paid for a place in this list, and none of the links here are affiliate links.
What to do next
Start with the two published prices and get scoped quotes from two of the quote-only providers at your real endpoint count — three numbers, all for the same 50 endpoints, is enough to rank this list. Run a trial on your shortlist and check that alerts reach a human who acts without you chasing. If the security stack is sorted but new customers are not finding you, our monthly SEO service handles the visibility side — or compare providers in our guide to email security software. Once your tools are in place, find out what's holding your rankings back.
Your stack only works if people find you
SerpAstra fixes what keeps your site off page one and makes it easy for AI assistants to recommend.
Get a free audit→Sources we checked (17)
- Huntress pricing — huntress.com/pricing (checked November 7, 2026)
- Blumira pricing — blumira.com/pricing (checked November 7, 2026)
- CrowdStrike pricing — crowdstrike.com/en-us/pricing (checked November 7, 2026)
- Arctic Wolf — arcticwolf.com (checked November 7, 2026; no published price, custom quote)
- Sophos MDR — sophos.com (checked November 7, 2026; no published price, custom quote)
- Bitdefender MDR — bitdefender.com (checked November 7, 2026; no published price, custom quote)
- SentinelOne Vigilance — sentinelone.com (checked November 7, 2026; no published price, custom quote)
- Rapid7 MDR — rapid7.com (checked November 7, 2026; no published price, custom quote)
- Expel — expel.io (checked November 7, 2026; no published price, custom quote)
- Huntress Managed EDR reviews — g2.com (checked November 7, 2026)
- Arctic Wolf reviews — g2.com (checked November 7, 2026)
- Sophos MDR reviews — g2.com (checked November 7, 2026)
- CrowdStrike Falcon Endpoint Protection Platform reviews — g2.com (checked November 7, 2026)
- SentinelOne Vigilance Respond reviews — g2.com (checked November 7, 2026)
- Rapid7 Managed Detection and Response Services reviews — g2.com (checked November 7, 2026)
- Expel reviews — g2.com (checked November 7, 2026)
- Blumira Automated Detection & Response reviews — g2.com (checked November 7, 2026)
Shamim
Founder of SerpAstra
A full-stack SEO and digital marketer who spends most days on Local SEO for dental practices, AI search visibility and lead generation.
Frequently asked questions
What is the best MDR software for small business security?
Huntress is the best fit for most small businesses: a published price of $8.99/endpoint/month, a 24/7 human SOC included, and the highest G2 rating here at 4.8/5. Arctic Wolf is the better pick when flat-rate pricing matters most, and Blumira suits teams that want per-employee pricing with a free SIEM edition.
How much does MDR cost for a small business?
Only two vendors publish prices: Huntress at $8.99/endpoint/month and Blumira from $12/employee/month. The other seven sell on custom quotes. A 50-endpoint business pays $449.50 a month on Huntress list pricing, or $5,394 a year — treat that as the floor and compare quotes against it.
Is there a free MDR service for small businesses?
No full MDR service is free. Blumira is the only option here with a free tier — a free SIEM edition with 3 cloud integrations and 14 days of retention — and Huntress, CrowdStrike and Blumira all offer free trials. Every true 24/7 managed service in this list is paid from day one.
What is the difference between MDR and EDR?
EDR is software: an agent on each endpoint that detects and responds to threats, which your own team must watch. MDR is a managed service: the vendor's analysts watch the EDR around the clock, investigate alerts and contain threats for you. Small businesses usually need MDR, because EDR without a night shift leaves alerts unread.
Do I still need antivirus if I buy MDR?
MDR includes endpoint protection — Huntress bundles managed antivirus, CrowdStrike and SentinelOne bundle next-generation antivirus in their platforms — so you do not buy a separate antivirus as well. What MDR does not replace is email security, backups and patching, which stay separate. See our guide to email security software for the inbox side.
Can I switch MDR providers later?
Yes, but plan the move carefully. Most contracts run 12 months, so time the switch for renewal. Uninstall the old agent before installing the new one — two endpoint agents on one machine cause conflicts — and export your alert history first, since it does not carry over to the new provider.
Free SEO and AI visibility audit
Find out what is holding your rankings back
Send us your site. Within 2 business days you get a written audit, an AI visibility check and a short fix list ranked by impact. Free, with no contract attached.
Request my free audit→Related guides
 Email, SMS & Social MediaBest Email Security Software for 2026: 11 Options Compared by Use CaseCompare the 11 best email security software options for 2026 on price, phishing defense and BEC protection, with every price checked November 6, 2026.Read guide →
 IT, Security & DevOpsBest Antivirus Software Review for 2026: 10 Options Compared by Use CaseCompare the best antivirus software review picks for 2026: 10 suites with prices, renewal costs, free plans and device limits, checked November 6, 2026.Read guide →
 Digital Marketing & Ads11 Best Online Data Backup Services in 2026Compare the 11 best online data backup services on price, storage caps, device limits and encryption, with every price checked November 5, 2026.Read guide →